Major Sports Events Committee awards "M" Mark status to three events
The following is issued on behalf of the Major Sports Events Committee:
The Major Sports Events Committee (MSEC) has awarded "M" Mark status to the 2026 World Triathlon Cup - Hong Kong (November 7 and 8), the BLAST Premier Hong Kong Rivals 2026 (November 13 to 15) and the Bank of China (Hong Kong) Hong Kong-Zhuhai-Macao Bridge (Hong Kong Section) Half Marathon 2026 (November 15).
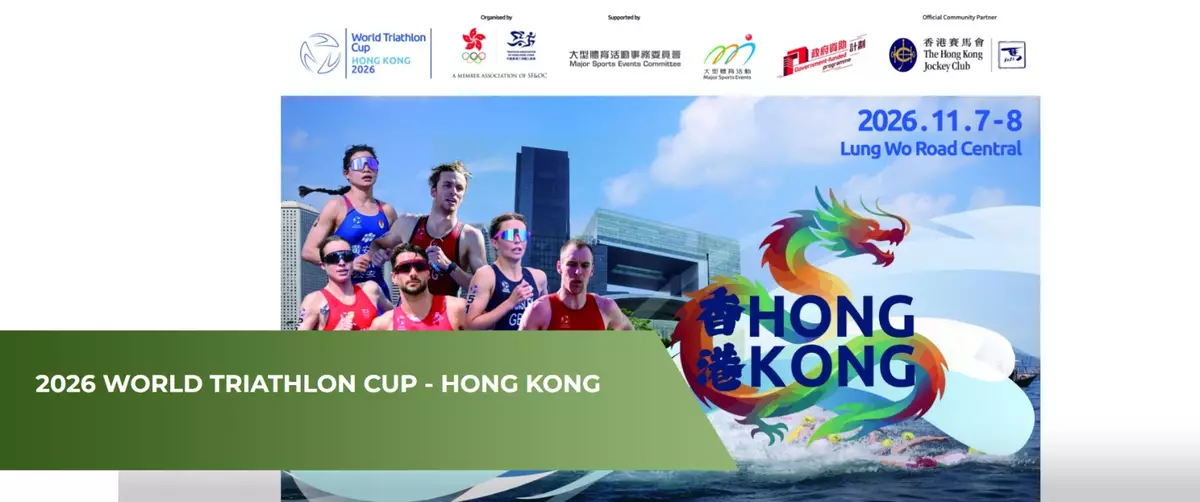
The 2026 World Triathlon Cup - Hong Kong. Photo source: triathlon.com.hk
The Chairman of the MSEC, Mr Wilfred Ng, said today (October 30), "We are very pleased to award 'M' Mark status to these three international sports events. The World Triathlon Cup allows athletes to showcase their incredible determination against the backdrop of Victoria Harbour and the streets of Central; the top-tier international esports event, the BLAST Premier Hong Kong Rivals, returns to AsiaWorld-Expo, drawing the attention of esports fans worldwide; and the Hong Kong-Zhuhai-Macao Bridge Half Marathon leverages a world-class landmark to highlight Hong Kong's unique appeal. Beyond attracting world-class athletes and international visitors to Hong Kong, these events will further consolidate Hong Kong's position as a centre for international sports events."
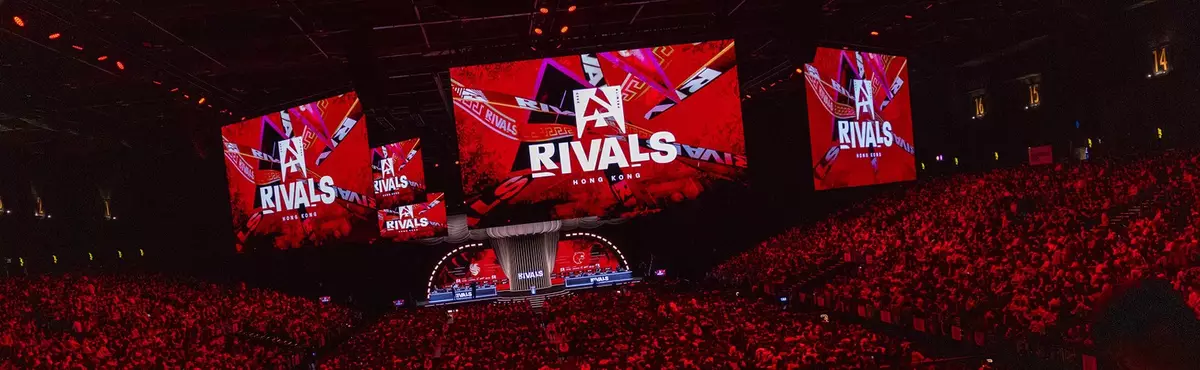
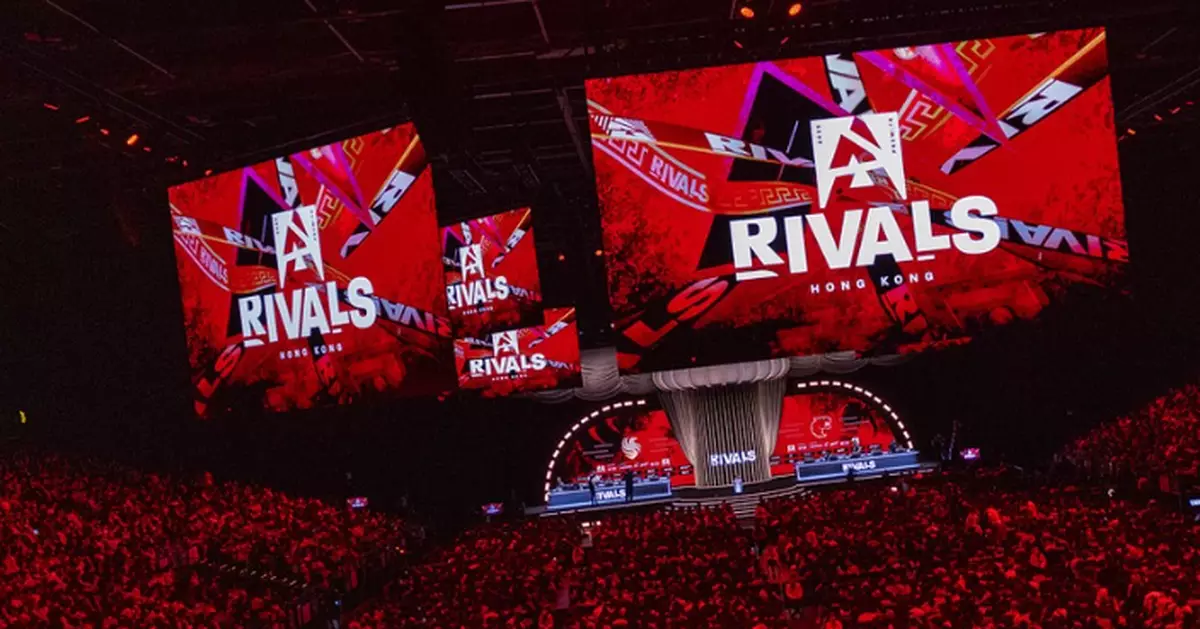
The BLAST Premier Hong Kong Rivals 2026. Photo source: mevents.org.hk
The "M" Mark System aims to encourage and help local National Sports Associations and private or non-government organisations to organise more major international sports events and nurture them into sustainable undertakings. Sports events meeting the assessment criteria will be considered for "M" Mark status by the MSEC. Funding support will also be provided to some events. The "M" Mark System aims to promote the development of major sports events, cultivate a sustainable sporting culture, enhance Hong Kong's image as a centre for major international sports events and bring tangible economic benefits to the community.
The Bank of China (Hong Kong) Hong Kong-Zhuhai-Macao Bridge (Hong Kong Section) Half Marathon 2026. Photo source: hzmb-halfmarathon.com
For details of "M" Mark events, please visit www.mevents.org.hk.
Hospital Authority responds to Office of Privacy Commissioner for Personal Data investigation report
The following is issued on behalf of the Hospital Authority:
The spokesperson for the Hospital Authority (HA) said today (October 30) that the HA notes the Office of the Privacy Commissioner for Personal Data (PCPD) has completed the investigation, and published the report today, regarding a suspected incident of patient data theft and the unlawful uploading of the data onto a third-party platform in the Kowloon East Cluster (KEC) in April this year. The HA accepts the investigation findings and recommendations, and will take appropriate action to seriously follow up on them. The HA will continue to strengthen its security of information system to ensure that hospital operations, patient services and personal data security are stringently protected.
In April this year, the HA's routine surveillance system detected a suspected incident of patient data theft in the KEC. The incident was an isolated event involving the management of data access control of a contractor during maintenance works in a peripheral clinical system, resulting in the theft of some patient data. The HA attaches great importance to the incident and had proactively reported it to Police and the PCPD in a timely manner. The Police subsequently arrested a staff member from the contractor on suspicion of access to a computer with dishonest intent. The HA has been fully co-operating with Police and the PCPD in the investigation. As the Police's criminal investigation is ongoing, it is not appropriate to further comment on the incident at this stage.
The HA takes the PCPD's recommendations on the protection of personal data seriously. Following the incident, the KEC immediately put in place a series of measures and conducted a comprehensive review, implementing a comprehensive strategy to strengthen the security of information system and oversight of contractors, including the procedures recommended by the PCPD, to prevent unauthorised access to the personal data of patients and staff through system maintenance work. The measures include:
- strictly requiring that whenever contractor personnel access the system on-site, they must be accompanied by duly authorised hospital information technology (IT) staff, with records kept of the contractor personnel's identity, purpose of access, time of operation, and equipment brought in and taken out;
- regularly auditing data access of the information systems concerned, and requiring contractors to submit audit reports to the HA periodically, reporting any anomalous, unauthorised or suspicious activities;
- strengthening oversight of contractors' access rights, configuring data access rights according to roles and functions, restricting use to authorised personnel and approved circumstances, and allowing data exports only under specifically approved circumstances; and
- regularly conducting independent security risk assessments and audits of the systems concerned by the cluster's IT department together with the Information Technology and Health Informatics Division of HA Head Office, in accordance with the HA Information Security Policy.
The KEC has previously informed and expressed an apology to the patients and staff affected through different channels.
The spokesperson emphasised that the HA has always attached great importance to the security of information systems and personal data privacy. The HA will continue to monitor the operation of its information systems around the clock and, should any anomaly be detected, appropriate contingency measures to safeguard the privacy of patients and staff will be taken promptly. The HA will also maintain close liaison with the PCPD and other law enforcement agencies, as well as professional cybersecurity organisations, to exchange security information and intelligence; continuously enhance system security; strengthen internal training, data management policies and guidelines; regularly conduct tests and reviews; and adopt up-to-date security technologies and solutions to effectively prevent any unlawful acts.
Source: AI-found images