
China's 2026 Cybersecurity Week opened on Monday in Jinan, capital city of east China's Shandong Province, with the release of the AI Safety Governance Framework 3.0 and the unveiling of several other cybersecurity research and development achievements.
The event also released the 2026 Test Results for AI Technology-enabled Cybersecurity Applications and a list of consumer-grade networked camera products that have completed cybersecurity labeling registration.
The cybersecurity week is jointly organized by 10 government departments and organizations, including the Cyberspace Administration of China, the Ministry of Industry and Information Technology and the Ministry of Public Security.
Running from Sept 14 to 20, this year's event is themed "Cybersecurity for the people, cybersecurity depends on the people -- safeguarding cybersecurity in the intelligent era".
The newly released AI Safety Governance Framework 3.0 carries forward the approach of placing equal emphasis on development and security, expanding the governance perspective from a single technical link to the entire process covering data, algorithms, models, applications and supply chains.
"The most core changes are in two aspects. The first is that risk categories have become more specific. We used a dedicated chapter to specifically explain the new categories of risks such as AI agent security risks and risks impacting cybersecurity, and for the first time adopted a special column to popularize knowledge on new types of security risks. The second is that governance measures have become more systematic. We systematically integrated comprehensive governance measures and added the building of a flexible, dynamic and controllable sandbox regulatory environment. These changes fully respond to the new security risks brought by the development of AI technology and new forms of application," said Li Yangchun, deputy director of the Institute of Informatization, the Chinese Academy of Cyberspace Studies.
The newly released AI Safety Governance Framework 3.0 further clarifies the responsibilities of all parties and promotes the formation of a governance framework that coordinates the roles of government regulation, primary corporate responsibility, industry self-discipline, social supervision and international cooperation.
"From the perspective of industry organizations, first, some typical casebooks [on AI security governance] can be worked out for reference by all Party A institutions and users. Second, the advantages of industrial organizations can be brought into play by presenting reports on the relevant events, notifications and some sharable knowhow to Party A institutions and security vendors. And third, the capacities of users and security vendors can be integrated to form the relevant group standards, and even relevant industry standards and national standards," said Tang Ning, executive director of the Cybersecurity Association of China.
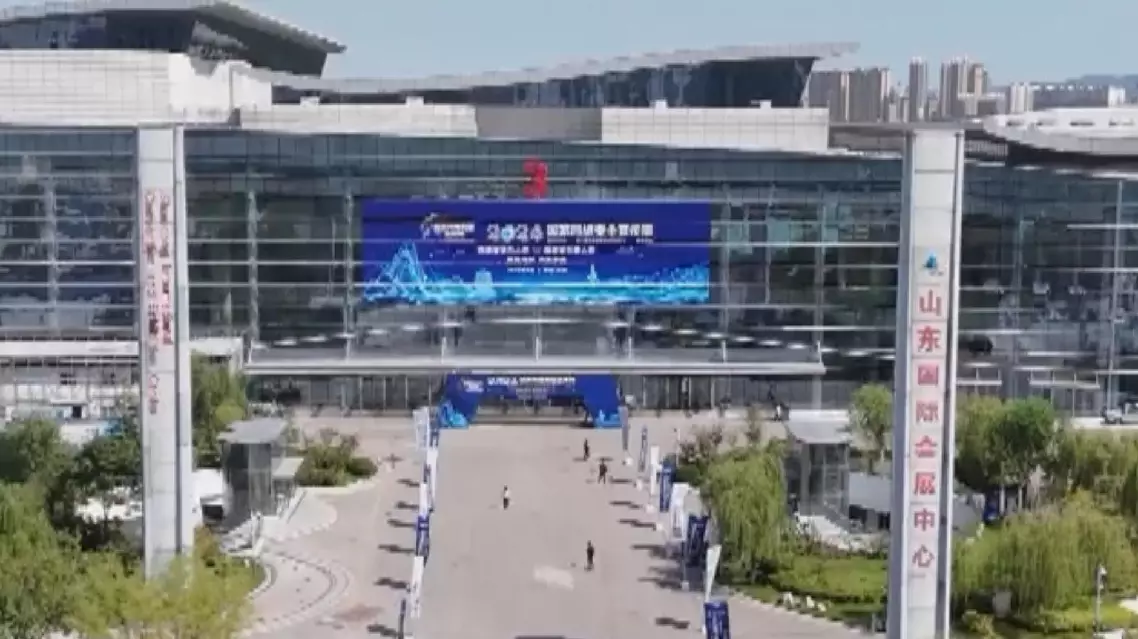
China unveils AI Safety Governance Framework 3.0